Safe, pull-based deployment
Ship new releases to servers that never accept incoming connections.
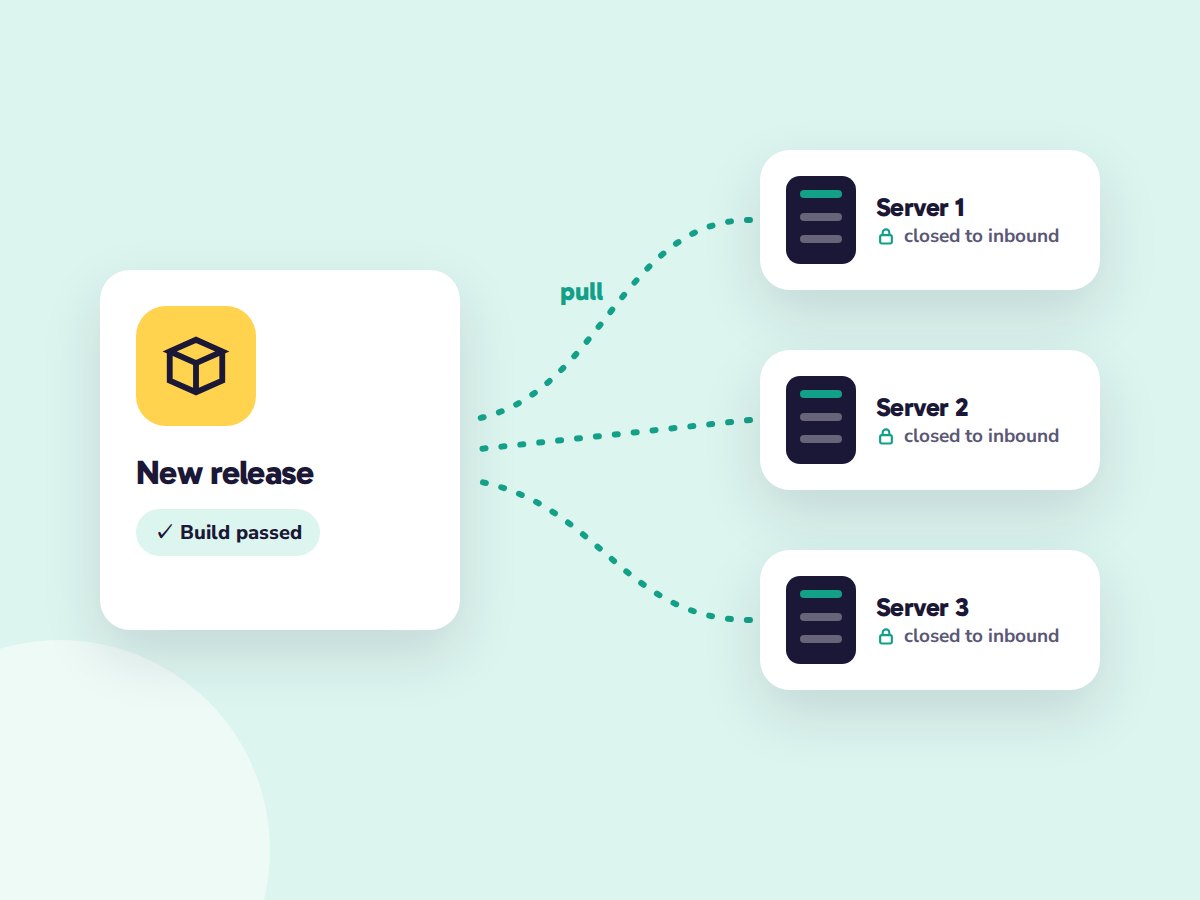
Opening a server to receive deployments also opens it to attackers. With pull-based deployment, servers fetch approved releases themselves, so they stay closed to the outside world and still update automatically.
Why teams love it
What it does for you
Smaller attack surface
Servers accept no inbound connections for deployment.
Works with your CI
Releases flow from the build system you already use.
Clear history
Every release is recorded from build to rollout.
A great fit for
- Teams with servers behind strict firewalls
- Regulated environments
- Edge and on-site servers
Example uses
- Update servers on customer sites without a VPN
- Roll out releases to a fleet in stages
- Keep production closed to inbound traffic
Ways to get it
Pick what suits you
Running in day-to-day use. Ready to license, deploy and support.
License it
Use it in your own product, on terms shaped around your market.
Pilot it with us
Try it in your world, with our engineers right beside your team.
Let us run it
A complete solution with integration and ongoing support, or a managed service.
Related services: Infrastructure and security
Curious about safe, pull-based deployment?
Tell us what you're building and we'll share how this could help.